In today’s digital age, the protection of personal data is paramount, especially for businesses operating within the European Union. The General Data Protection Regulation (GDPR) has set stringent guidelines to ensure that personal information is handled with care and confidentiality. One critical aspect of GDPR compliance is the secure destruction of documents containing sensitive data. Failing to comply can lead to severe penalties and damage to your business’s reputation. This guide will help business owners and office managers understand what documents must be shredded by law and how to effectively comply with GDPR regulations.
What Immediate Steps Should You Take for GDPR Document Destruction?
Ensuring GDPR compliance in document destruction requires immediate attention to your current data handling processes. Begin by conducting a thorough audit of all documents stored within your business. Identify those containing personal data, and evaluate whether they are still necessary for your operations. For more information, refer to the document destruction guidelines.
Documents You Must Shred by Law
- Employee records containing personal data
- Customer contracts and agreements
- Financial statements and reports
- Medical records and personal health information
- Legal documents with personal identifiers
- Old tax records and invoices
- Any document with sensitive personal information
Understanding GDPR Requirements for Document Destruction
The GDPR mandates that personal data should be processed and stored securely, and when no longer needed, it must be disposed of in a manner that ensures the data cannot be reconstructed or retrieved. This means that simply discarding documents in the trash is not sufficient. Businesses must implement a secure shredding process to protect the data they handle. This requirement extends to both physical and digital documents, emphasizing the need for comprehensive data protection strategies.
To comply with GDPR, businesses must first identify all documents that contain personal data. This includes any information that can be used to identify an individual, such as names, addresses, financial details, and more. Once identified, these documents should be securely shredded using an appropriate method that aligns with the level of sensitivity of the data. Regular audits and updates to document retention policies are also crucial in maintaining compliance.


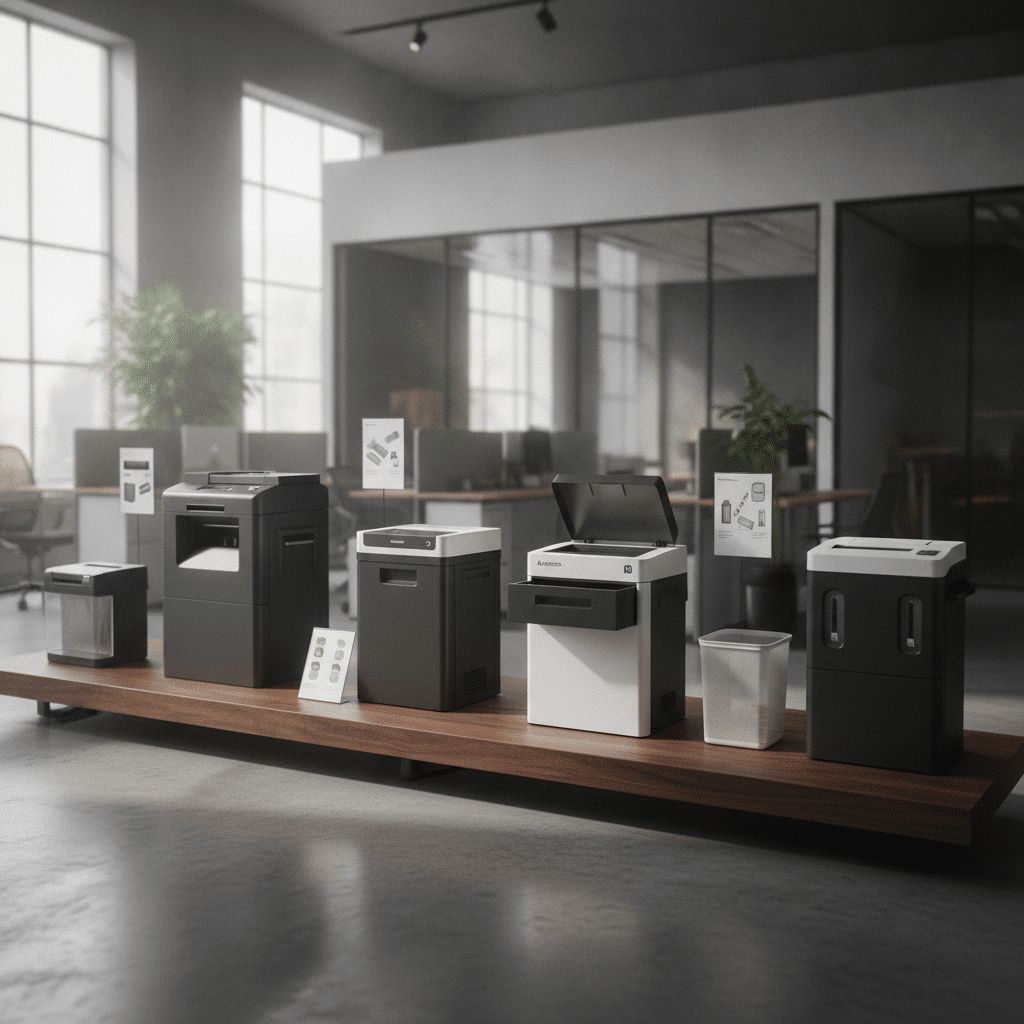
Viking Shredder 12 Sheets Cross Cut Security Level P-3 25 L OS1201D

Viking Shredder 18 Sheets Cross Cut Security Level P-4 28 L OS1801CI

Viking Auto Feed Shredder 120 Sheets Micro Cut Security Level P-4 23 L C233-B

Viking Shredder 10 Sheets Cross Cut Security Level P-4 10 L OS1006C

Viking Shredder 9 Sheets Micro Cut Security Level P-5 20 L OS901Mi
Implementing a Shredding Policy for GDPR Compliance
Creating a shredding policy is a vital step toward GDPR compliance. This policy should outline the types of documents that require shredding, the frequency of shredding, and the methods used. It should also designate responsible personnel for overseeing the shredding process and maintaining records of destroyed documents. By having a clear policy in place, businesses can ensure that all employees understand their roles in protecting personal data and adhering to GDPR standards.
Moreover, businesses should invest in high-quality shredders that meet the security requirements for the types of documents they handle. Training employees on the correct use of shredders and the importance of data protection is equally important. Regularly reviewing and updating the shredding policy will help to address any changes in data handling practices or regulatory requirements, ensuring ongoing compliance with GDPR.
Comparison Table of Shredders for GDPR Compliance
| Shredder Type | Security Level | Best For |
|---|---|---|
| Strip-Cut | Low | General documents |
| Cross-Cut | Medium | Confidential documents |
| Micro-Cut | High | Sensitive documents |
| High-Security | Very High | Top-secret documents |
Conclusion: Ensuring GDPR Compliance Through Secure Document Destruction
GDPR compliance is not just a legal obligation but a crucial aspect of maintaining trust with your clients and employees. By implementing a robust shredding policy and investing in the right equipment, businesses can effectively protect sensitive data and avoid the severe penalties associated with non-compliance.
Remember, the key to GDPR compliance is understanding the regulations, identifying the documents that require secure disposal, and consistently applying best practices in document destruction. By doing so, you safeguard your business and contribute to a culture of data protection and privacy.
Frequently Asked Questions About GDPR and Document Destruction
What is considered personal data under GDPR?
Personal data encompasses any information relating to an identified or identifiable person. This includes names, identification numbers, location data, online identifiers, and factors specific to the physical, physiological, genetic, mental, economic, cultural, or social identity of a person.
How often should documents be shredded to comply with GDPR?
The frequency of shredding depends on the nature of the documents and the data retention policies of your business. Regular shredding, such as weekly or monthly, is recommended for documents that are no longer needed. However, immediate shredding should occur when documents reach the end of their retention period and are no longer necessary for business operations.
Can digital documents be shredded under GDPR?
While digital documents cannot be physically shredded, they must be securely deleted in a manner that ensures they cannot be recovered. This can be achieved through the use of specialized software that permanently erases data from digital storage devices, ensuring compliance with GDPR.
What are the penalties for non-compliance with GDPR shredding requirements?
Non-compliance with GDPR shredding requirements can result in significant fines, reaching up to 4% of a company’s annual global turnover or €20 million, whichever is higher. Beyond financial penalties, businesses may also suffer reputational damage, loss of client trust, and legal actions from affected individuals.
Are there any specific industries that need to be more vigilant about document shredding?
Industries handling large volumes of personal data, such as healthcare, finance, and legal sectors, need to be particularly vigilant about document shredding. These industries often deal with sensitive information that, if mishandled, can lead to severe consequences for both the business and the individuals involved.